
Information Security
SAI Hardware Requirement
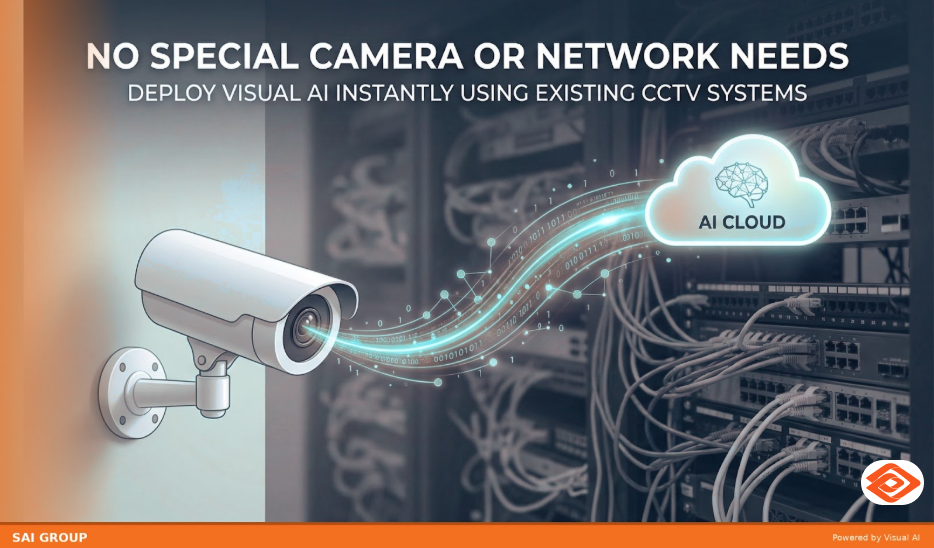
No Special Camera or Network Needs
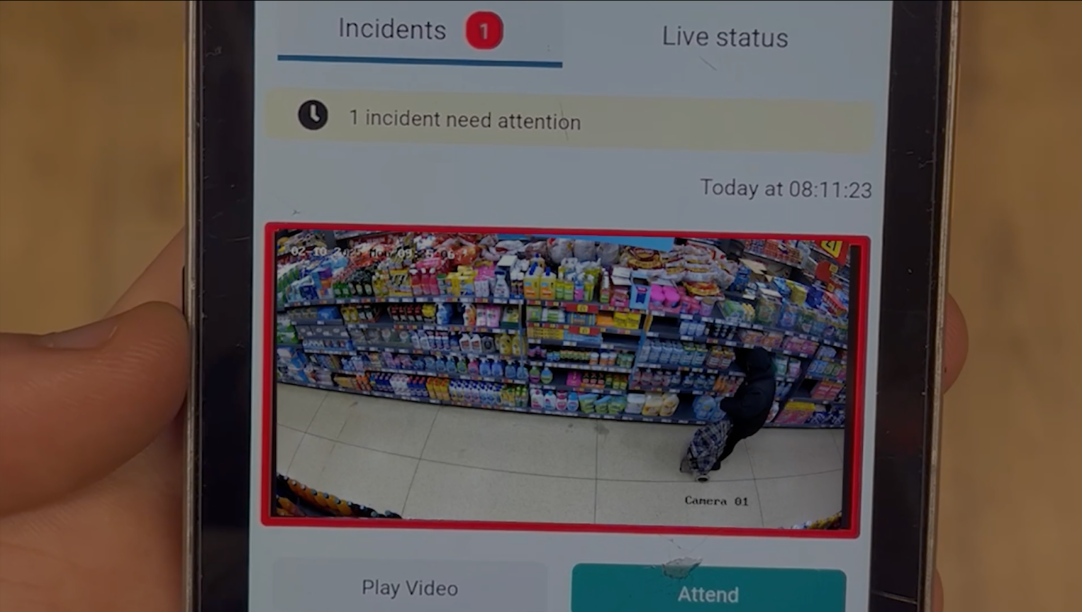
White Labeled Alerts App
Cloud‑Native Solution
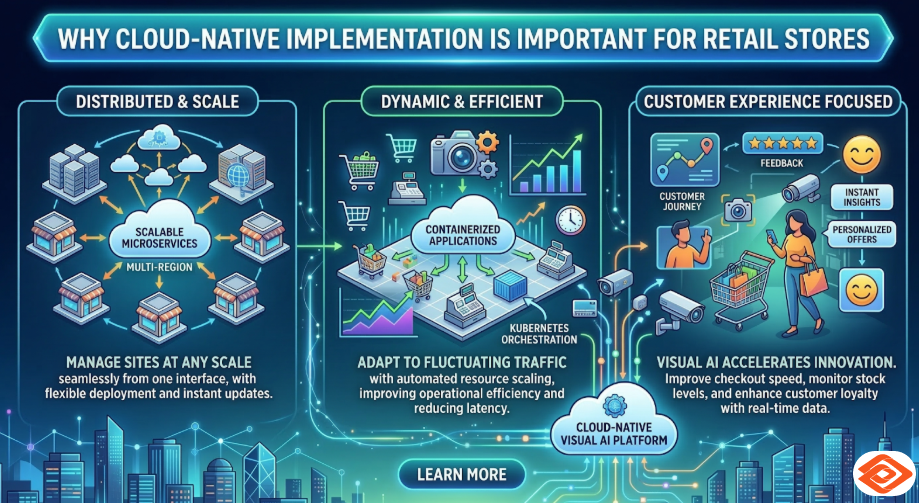
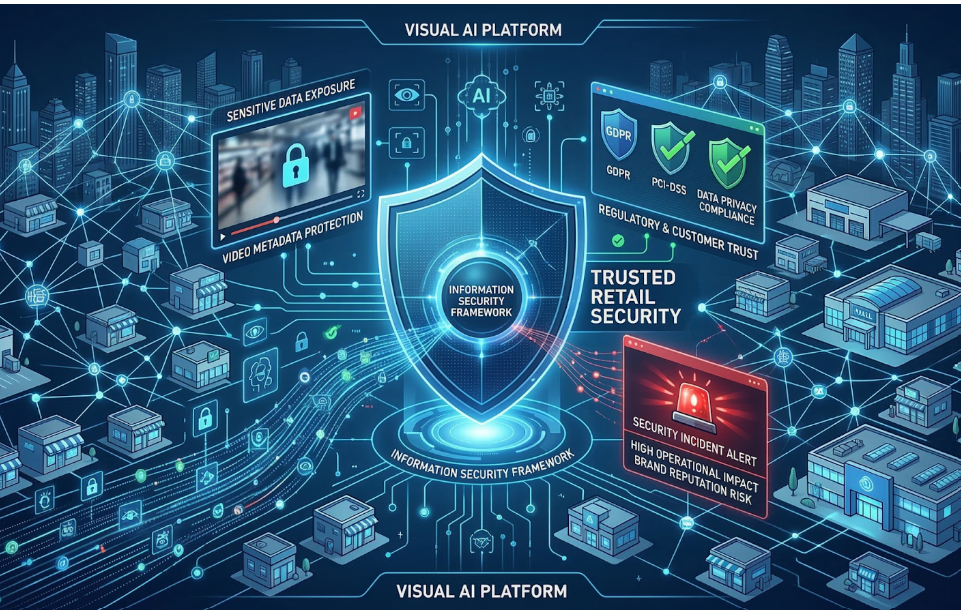
Information Security
Detailed view: Security, Privacy and Resilience by Design
SAI One protects the data, credentials and infrastructure behind the continuous visual intelligence generated through our patented Vision Language Model technology.
SAI One is designed to operate visual AI securely across distributed environments, from retail estates and fuel & convenience sites to other complex operational settings.
Data is encrypted in transit and at rest, with controlled access to sensitive credentials and security controls built across the platform. Compliance is continuously monitored through Vanta, while CrowdStrike-managed detection and response (MDR) provides ongoing monitoring for security threats.
The result is a security approach built around the same principle as SAI One itself: make complex operations easier to manage, without compromising trust, privacy or resilience.
Why Information Security Matters for Modern AI Operations
Information security becomes more complex when visual AI operates across cameras, edge devices, cloud services, applications and operational systems. For large retail estates, that means security has to extend beyond a central data environment.
The same applies to other distributed environments where visual intelligence operates across many physical locations.
- •Distributed infrastructure: Stores, sites, cameras and edge devices operate across multiple locations, creating a broader security surface than a conventional centralised environment.
- •Sensitive operational data: Video streams, operational metadata, system credentials and platform data require controlled access and appropriate protection.
- •Privacy and regulatory obligations: Organisations need clear controls around how data is accessed, processed, stored and protected, particularly where visual data is involved.
- •Operational continuity: A security incident can affect more than data. It can interrupt operations, create investigation workloads and affect customer and colleague confidence.
- •Growing AI governance requirements: As AI becomes part of operational decision-making, organisations need governance covering security, privacy, accountability and responsible AI management. ISO 42001 provides an internationally recognised framework for managing AI systems and their associated risks.
SAI One addresses these requirements through controlled credential access, continuous compliance visibility, managed threat detection and a security framework built around the platform.
How Security Is Built Into SAI One
Controlled Security Credentials
Visual AI platform security begins with protecting the credentials used across the SAI One environment through controlled access mechanisms.
Access is restricted to authorised users and services, reducing the risk of unauthorised use, leakage or accidental exposure.
This supports secure connections across cameras, edge infrastructure, backend services and other integrated systems.
By treating credentials as sensitive assets, SAI One maintains consistent security controls across distributed deployments.
Continuous Compliance Visibility with Vanta
Security and compliance should not depend on an annual audit cycle.
SAI uses Vanta for continuous compliance monitoring, giving teams ongoing visibility into the organisation's security and compliance posture.
This supports:
- •Continuous security visibility
- •Early identification of control gaps
- •Ongoing evidence collection
- •Faster audit preparation
- •Clearer compliance oversight as deployments grow
This approach turns compliance into an ongoing operational process rather than a periodic exercise.
Managed Threat Detection and Response
SAI uses CrowdStrike-managed detection and response (MDR) to monitor for suspicious activity and security incidents.
The service provides an enterprise-grade threat protection layer around the platform, supporting:
- •Proactive threat detection
- •Security incident investigation
- •Expert-led response
- •Ongoing monitoring for suspicious activity
- •Reduced exposure to operational disruption
This complements SAI One's platform-level controls with managed security monitoring focused on active threats. Together, these layers create a defence approach designed to identify and address threats before they can disrupt operations or compromise sensitive systems.

SOC 2
Trust Controls

ISO 27001
Information Security
ISO 42001
AI Management

GDPR
Data Privacy
UK Cyber Essentials
Cyber Security
ISO 27701
Privacy Management
ISO 22301
Business Continuity
SAI One Is The Most Certified Vision AI Platform
Your data stays fully encrypted both during transit and at rest, supported by independently assessed security controls and recognised standards covering information security, AI management, data privacy, cyber security and business continuity. These include:
- •SOC 2
Trust and Control
SOC 2 examines the controls an organisation has in place for areas such as security, availability, processing integrity, confidentiality and privacy.
Why it matters: It provides independent assurance that relevant controls are designed and operating effectively, giving customers greater confidence in how systems and data are managed. - •ISO 27001
Information Security
ISO 27001 sets the requirements for an Information Security Management System (ISMS), covering how an organisation identifies, manages and continually improves information security risks.
Why it matters: It provides a structured approach to protecting information across people, processes and technology, supporting confidentiality, integrity and availability. - •ISO 42001
AI Management
ISO 42001 provides a management framework for the responsible development, provision and use of AI systems, including the management of AI-related risks and opportunities.
Why it matters: For an AI platform, it provides a structured approach to AI governance, supporting responsible use, transparency, traceability and ongoing risk management. - •GDPR
Data Privacy
GDPR sets requirements for how organisations collect, use, store and protect personal data, with principles covering lawfulness, transparency, purpose limitation, data minimisation, security and accountability.
Why it matters: Visual AI operates in environments where privacy needs to be considered alongside security. GDPR provides the regulatory framework for responsible handling of personal data. - •UK Cyber Essentials
Cyber Security
Cyber Essentials is a UK Government-backed scheme focused on five core technical controls: firewalls, secure configuration, security updates, user access control and malware protection.
Why it matters: These controls address common routes used in cyber attacks and establish a practical baseline for protecting systems and services. - •ISO 27701
Privacy Management
ISO 27701 provides requirements and guidance for establishing and continually improving a Privacy Information Management System (PIMS), with a focus on personally identifiable information.
Why it matters: It gives organisations a structured approach to managing privacy responsibilities, demonstrating accountability and strengthening personal data protection. - •ISO 22301
Business Continuity
ISO 22301 provides the framework for a Business Continuity Management System (BCMS), covering preparation for, response to and recovery from disruptive incidents.
Why it matters: Security is also about keeping critical operations running when disruption occurs. ISO 22301 provides a structured approach to resilience and recovery.
Frequently Asked Questions
SAI One uses controlled access mechanisms to protect credentials used across the platform, reducing the risk of unauthorised access, leakage or accidental exposure.
SAI uses Vanta to maintain ongoing visibility into its security and compliance posture, supporting early identification of gaps and faster preparation for audits and assessments.
CrowdStrike provides managed detection and response, monitoring for suspicious activity and security incidents and supporting expert-led investigation and response.
AI data protection is supported through encryption in transit and at rest, with access to sensitive systems and credentials controlled through defined security mechanisms.
Yes. SAI One incorporates privacy controls and governance designed around applicable data protection requirements. SAI also holds ISO 27701 certification for privacy information management.
SAI's AI governance framework is supported by ISO 42001, the international standard for AI management systems. It provides a structured approach to managing risks and responsibilities associated with AI.
Yes. The platform's security approach is built to support deployments spanning multiple locations, cameras, edge devices, integrations and operational environments.
SAI's security framework includes business continuity management aligned with ISO 22301, supporting preparation, response and recovery from disruptive incidents.